kubernetes kubernetes/kcna kubernetes/networking
👉 TLS
Core Idea
Kubernetes components talk over TLS: every service presents a server certificate and every client presents a client certificate, so each side proves who it is.
- Purpose and use of TLS certificates in the cluster, plus the key types of certificates involved.
- The certificate workflow, with creation shown through an API server TLS configuration example.
- TLS for ingress, including automatic certificate management.
TLS in K8s
TLS (Transport Layer Security) certificates are essential for securing communication between components in a Kubernetes cluster. They ensure data integrity, confidentiality, and authentication.
The two primary requirements are to have all the various services within the cluster to use server certificates and all clients to use client certificates to verify they are who they say they are.
- Server Certificates for Servers
- Client Certificates for Clients
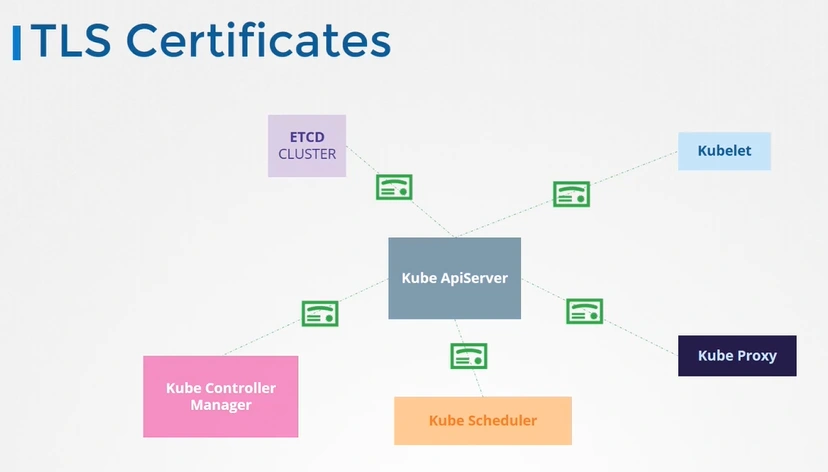
Purpose of TLS Certificates in Kubernetes
- Encrypt Communication: Secure communication between cluster components and external users by encrypting data.
- Authentication: Validate the identity of components and users in the cluster.
- Data Integrity: Prevent tampering with data during transmission.
Use of TLS Certificates in Kubernetes
TLS certificates are primarily used to secure:
- Cluster Components:
- API Server: Communicates securely with
kubectl, kubelets, and other components. - etcd: Ensures secure communication between the API server and the etcd database.
- Kubelets: Secures communication between the kubelets and the API server.
- API Server: Communicates securely with
- Client Authentication:
- Certificates are used to authenticate users or applications accessing the cluster.
- Users provide a client certificate to prove their identity.
- Ingress Controllers:
- TLS certificates secure connections between end-users and applications exposed via ingress.
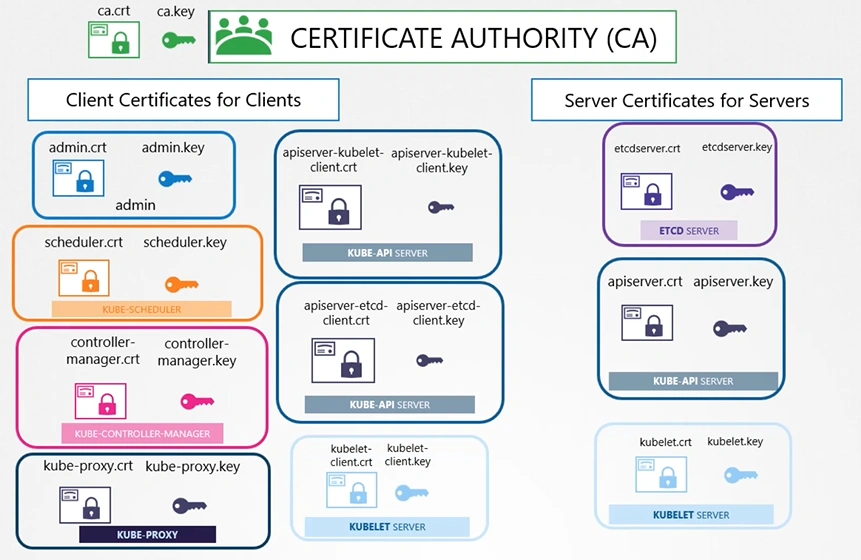
Key Types of Certificates in Kubernetes
- Server Certificates: Used by components like the API server to prove their identity to clients.
- Client Certificates: Used by users, services, or components to authenticate to the API server.
- CA Certificates: A Certificate Authority (CA) signs other certificates. Kubernetes uses a root CA to sign server and client certificates.
TLS Certificate Workflow
- Generate a Certificate Authority (CA):
- The CA is used to sign other certificates.
- Kubernetes often includes a default CA managed by kubeadm or other tools.
- Generate Certificates:
- Create private keys and Certificate Signing Requests (CSRs) for each component.
- Sign the CSRs using the CA to issue certificates.
- Configure Certificates:
- Add certificates and keys to appropriate components (e.g., kube-apiserver, kubelet, etcd).
- Pass certificates as flags or mount them into containers.
- Renew Certificates:
- Certificates have a validity period and must be renewed periodically.
- Kubernetes provides mechanisms for automatic certificate rotation.
Certificate Creation
🌟 07-TLS-in-Kubernetes-Certificate-Creation
🌟 08-View-Certificate-Details
🌟 11-Certificate-API
Example: API Server Configuration with TLS
- Certificates are specified as flags when starting the kube-apiserver:
kube-apiserver \
  --tls-cert-file=/path/to/server.crt \
  --tls-private-key-file=/path/to/server.key \
--client-ca-file=/path/to/ca.crt--tls-cert-file: Server certificate.--tls-private-key-file: Private key for the server certificate.--client-ca-file: CA certificate to validate client certificates.
TLS for Ingress
👉 Ingress
👉 Kubernetes Ingress Tutorial
- TLS certificates are also used in ingress resources to secure application access:
apiVersion: networking.k8s.io/v1
kind: Ingress
metadata:
  name: my-app
spec:
  tls:
  - hosts:
    - my-app.example.com
    secretName: my-app-tls
  rules:
  - host: my-app.example.com
    http:
      paths:
      - path: /
        pathType: Prefix
        backend:
          service:
            name: my-app-service
            port:
              number: 80
The my-app-tls secret contains the certificate and key.
Automatic Certificate Management
- kubeadm: Automates CA and certificate generation during cluster setup.
- cert-manager: A Kubernetes add-on that simplifies issuing and renewing certificates using external CAs like Let’s Encrypt.